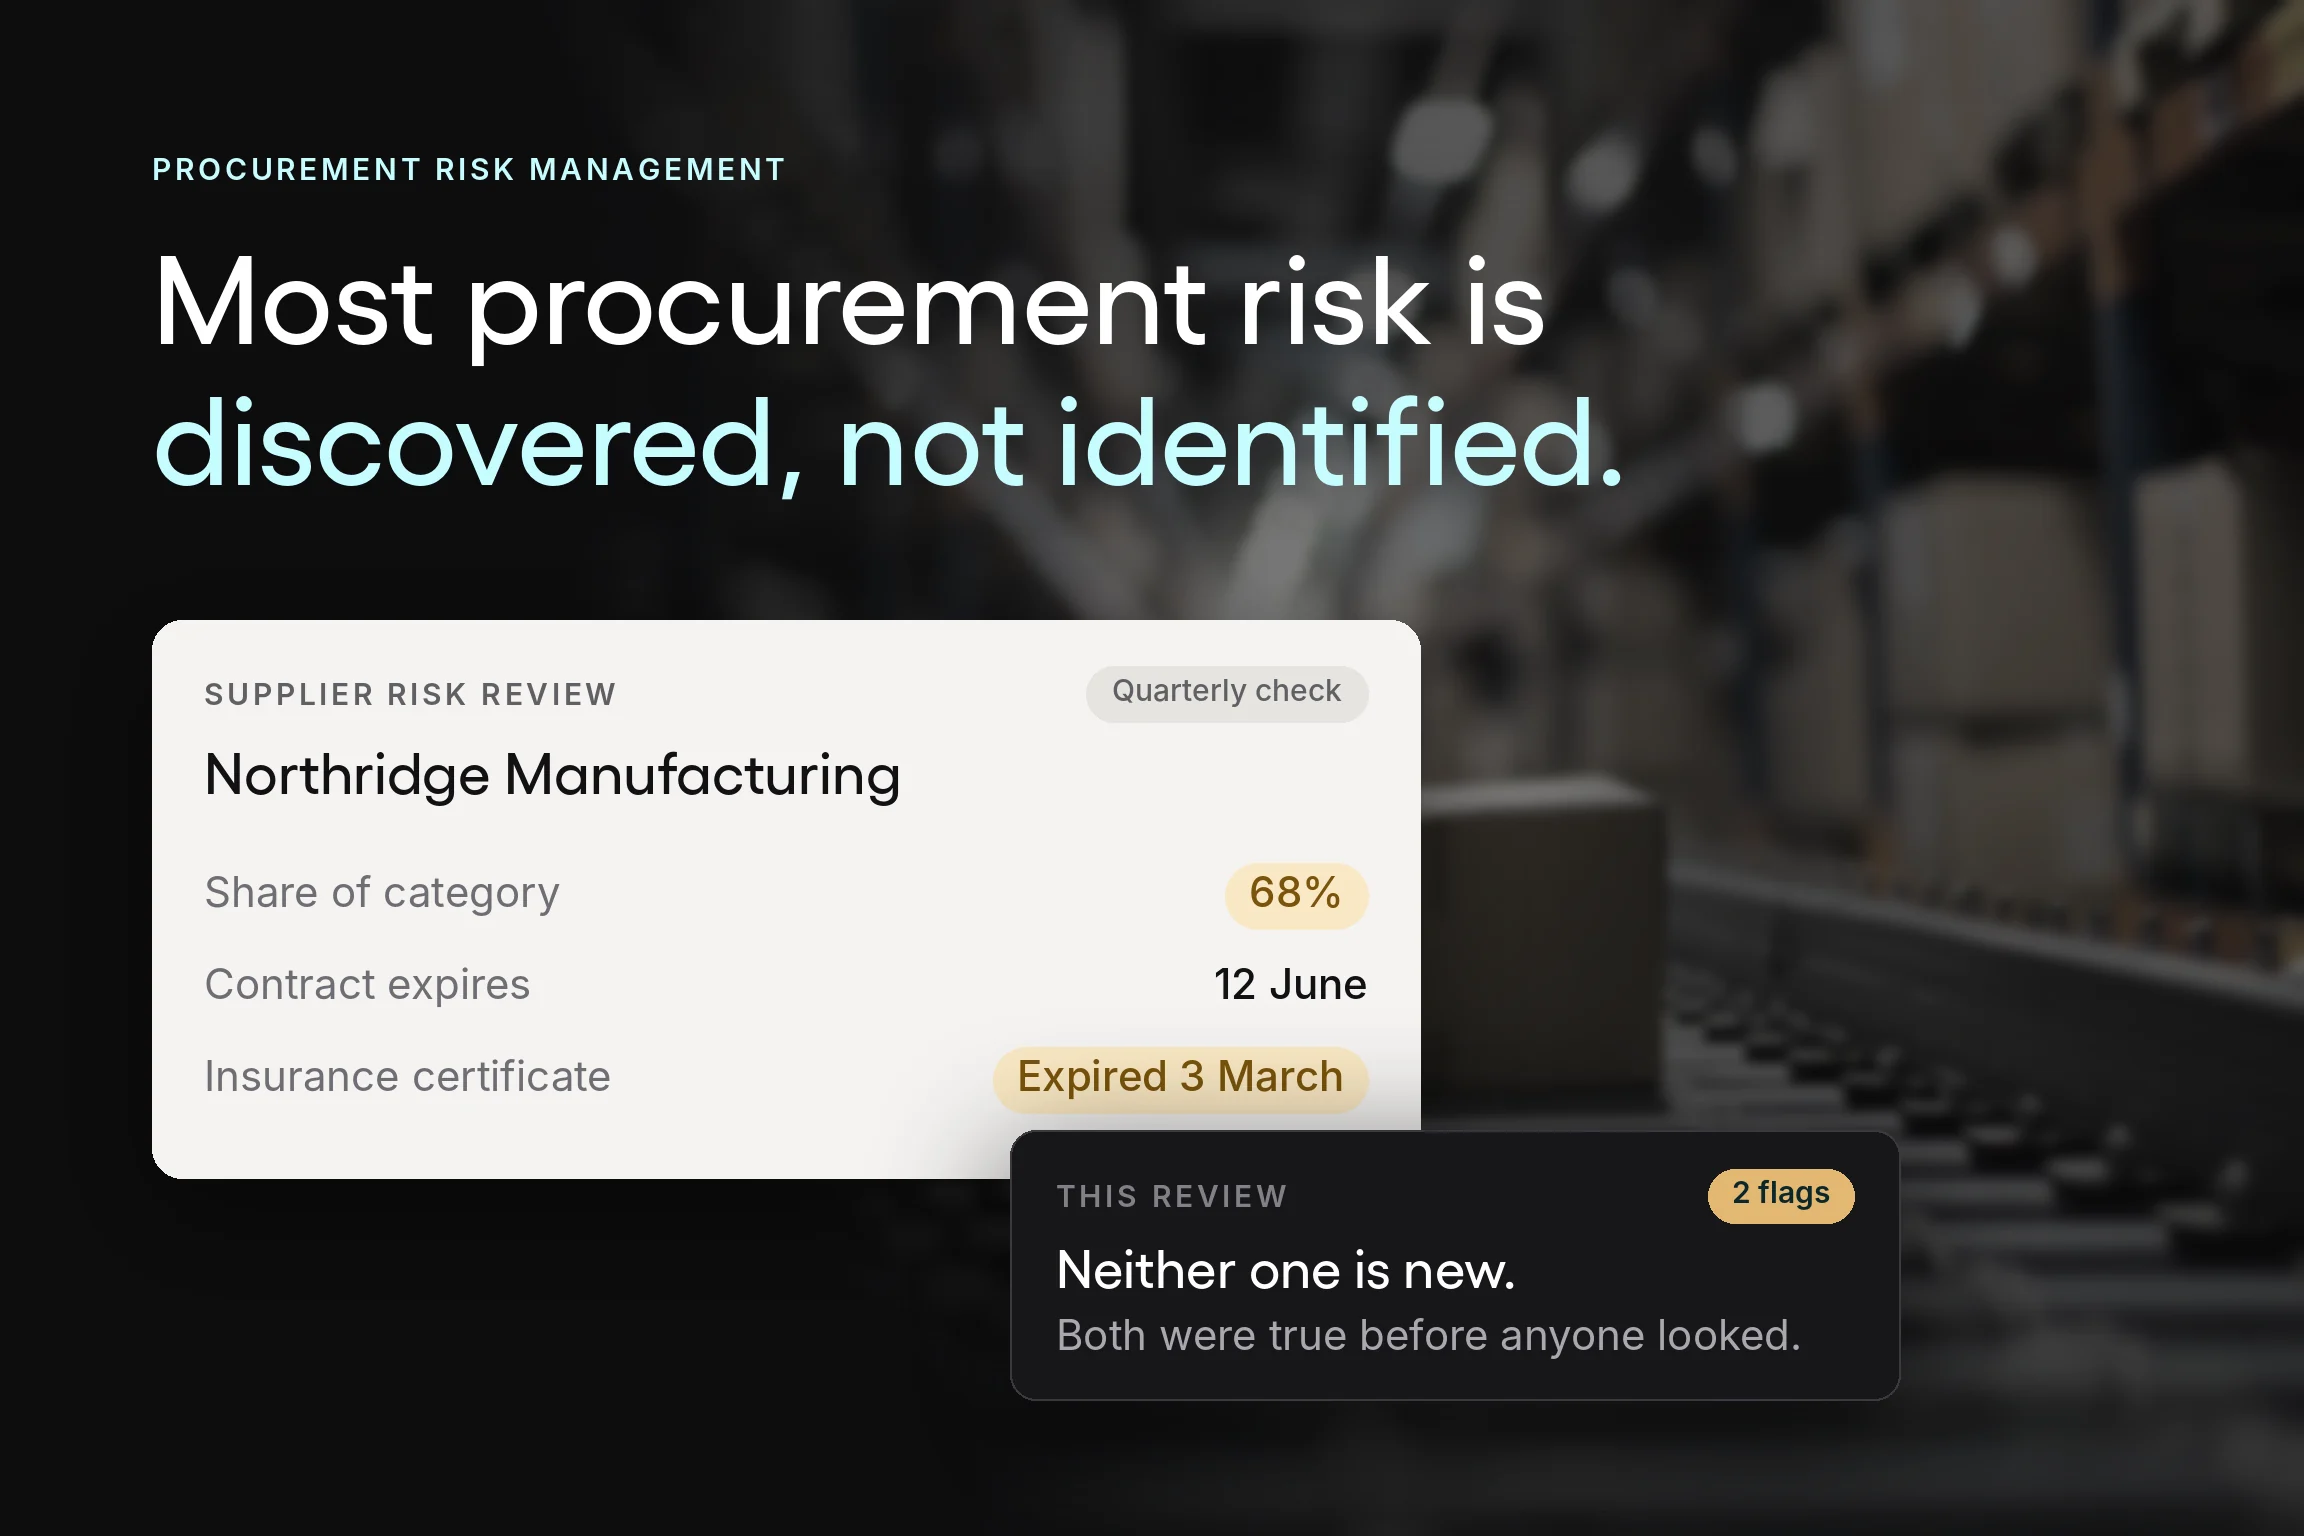

Most procurement risk is discovered rather than identified. A supplier misses a delivery, and you find out there was no second source. An invoice arrives with a price nobody agreed to, and you find out the contract expired in March. A regulator asks for documentation, and you find out the approval happened in a chat thread.
None of those are exotic failures. They are ordinary gaps in a process that worked fine at a smaller scale, and they share a single characteristic: the exposure existed long before anyone noticed it.
Procurement risk management is the discipline of finding those gaps on purpose, not by accident. This guide covers what procurement risk actually is, the main types of procurement risk and what each one looks like in practice, the risk factors that make an organization more exposed than its peers, how to handle contract risk specifically, and what a workable risk management process looks like for a team that does not have a dedicated risk function. Getting ahead of potential risks is less about prediction than about looking in the right places at the right time.
Key Takeaways
- Procurement risk management is a process, not a document. Identification, assessment, mitigation, and monitoring have to run continuously, because a risk register built once and filed is a snapshot of a situation that has already changed.
- Most procurement risks fall into six types, and organizations are rarely exposed evenly across them. Supplier, supply chain, market, compliance, operational, and financial risks each need different controls, so the first useful exercise is working out which two or three actually threaten your business.
- Visibility is the precondition for everything else. You cannot assess a risk you cannot see, which is why organizations running on manual processes and outdated data consistently discover problems later than those working from a live purchasing record.
- Proportionality keeps risk management sustainable. Applying the same scrutiny to a critical single-source supplier and a stationery vendor wastes the effort on the wrong relationships and is the most common reason a risk program quietly stops running.
What is procurement risk management?
Procurement risk management is the process of identifying, assessing, mitigating, and monitoring what can go wrong when an organization buys goods and services from third parties.
Procurement risks are the possibilities that procurement activity produces an unintended outcome or a costly consequence: a supplier fails, a price moves, a contract obligation is missed, a regulation is breached, or a purchase happens outside policy. They arise from inadequate supplier vetting, poor contract administration, weak internal controls, and external factors nobody in the business controls.
The key distinction is that risk management is not the same as problem solving. Solving a problem deals with something that has already happened. Effective risk management deals with something that has not, which means it depends entirely on whether the organization has a holistic view of its own purchasing activity before the event.
Why it matters to the business
The case for managing risk in procurement is usually made in terms of avoided cost, and that undersells it.
Risk management prevents unnecessary expenses and unplanned expenditures, which is real. It also reduces significant delays by identifying single points of failure before they fail, protecting business operations that depend on continuity more than price. It protects reputation, since supplier failures and compliance breaches become the buyer’s problem regardless of who caused them.
It strengthens supplier partnerships, because the discipline that produces good risk management, clear contracts, honest performance conversations, and reliable payment is the same discipline that produces collaborative relationships. It builds strong supplier relationships because suppliers behave differently toward predictable buyers. It also keeps the organization within its regulatory obligations and contractual commitments, which matters most in the public sector and in regulated industries where a breach is published rather than absorbed.
For most businesses, the strongest argument is simpler. Procurement decisions commit money and create obligations that outlast the person who made them. Someone should be checking what those obligations are.
The six most common procurement risks
Risk categories are useful only insofar as they change what you do. These six cover the field, and each one has a different control.
1. Supplier risk
Supplier risk is the exposure created by depending on a specific organization to deliver.
It shows up as financial instability at a supplier you rely on, capacity that cannot meet your volume, quality that drifts, inadequate vetting that lets an unsuitable vendor onto the approved suppliers list in the first place, and weak supplier relationships where communication gaps produce late deliveries and unfavorable terms nobody negotiated deliberately.
The control is due diligence before onboarding and continuous monitoring afterward, which a proper supplier management record supports. Supplier due diligence should assess financial health, operational capacity, insurance and certifications, and references from comparable customers. Continuous supplier evaluation, rather than an annual review, is what catches deterioration while there is still time to act.
2. Supply chain risk
Supply chain risk is exposure to disruption in the flow of goods, including from events far upstream of your direct supplier.
Supply chain disruptions occur for reasons unrelated to your supplier's competence, including extreme weather, natural disasters, public health events, labor shortages, transport failures, and manufacturing delays at a factory two tiers removed from anyone you have a contract with. A pandemic-scale event is the version everyone now plans for, but the routine version, a flood at a single component plant, is far more common and equally capable of stopping a production line.
The controls are visibility and redundancy. Supply chain visibility means knowing where your critical inputs actually originate, not just who invoices you for them. Redundancy means qualified alternate sources for the inputs you cannot operate without, and buffer stock for the ones where an alternate source cannot be qualified quickly. Both cost money, so apply them only where the potential impact justifies it. This is where risk planning stops being theoretical and starts being a budget conversation.
3. Market risk
Market risks are exposures to price and availability movements in the categories you buy.
Raw materials move on commodity cycles. Energy prices move on a combination of supply concentration and geopolitical factors, and those movements pass through into transport, manufacturing, and eventually your unit costs. Currency shifts change an overseas supplier's economics without either party doing anything. Increased costs arriving mid-contract are the visible symptom.
The controls are contractual and structural, and they belong in the procurement strategy rather than in a separate risk document: fixed-price or indexed terms where volatility is expected, longer agreements where you want price certainty, shorter ones where you expect prices to fall, and spend analysis good enough to tell you which categories are actually exposed. Many organizations hedge the wrong categories because nobody checked which ones carried the real risk exposure.
4. Compliance risk
Compliance risk is the exposure created when purchasing activity breaches a rule, whether external regulation or internal policy.
It covers regulatory violations, trade restrictions and sanctions that make a previously routine supplier relationship unlawful, sector-specific procurement rules, data protection obligations that follow the information you share with vendors, and fraud committed through poorly controlled supplier contracts. Regulatory changes arrive unexpectedly, which means compliance is a monitoring problem rather than a one-time check. Non-compliance leads to fines, canceled contracts, and reputational damage whose negative impact usually costs more than the penalty.
The control is making the rule the path of least resistance. The system applies approval thresholds rather than relying on memory, routes purchases to approved suppliers by default, and produces an audit trail as a byproduct of buying rather than assembling it afterward. Continuous due diligence on suppliers in regulated categories closes the remaining gap.
5. Operational risk
Operational risk is the exposure created by your own process.
Manual processes generate human error at every retyping. Outdated data leads to decisions made against last quarter’s prices and a supplier list nobody pruned. Organizations that lack visibility into committed spend discover overruns after the money is gone. Purchase orders raised after the invoice arrives, approvals recorded nowhere, and receiving that nobody logged all belong here.
This is the risk type most within your control and the one procurement leaders most often overlook, because it does not feel like risk. It feels like admin. But automating procurement processes reduces human error and delays more reliably than any amount of care, and a connected purchasing record is what makes the other five risk types visible in the first place.
6. Financial risk
Financial risk covers direct monetary exposure: cost overruns against budget, duplicate payments, fraudulent invoices, unfavorable payment terms accepted by default, and commitments made without authority.
Payment fraud deserves particular attention because the mechanism has shifted. The classic version was a fake invoice from a supplier that does not exist. The current version is a request to change the banking details of a supplier you genuinely use, which is harder to spot precisely because the relationship is real and the invoice is expected.
The controls are familiar and effective: budget checks before approval rather than after invoicing, three-way matching of invoice against purchase order and receiving record, segregation of duties so the person who approves a supplier is not the person who approves their invoice, and verified banking details captured at onboarding so a change request has something to be checked against.
The last of those is worth doing even if you do nothing else on this list. A supplier record with verified banking details turns a change request from a judgment call into a comparison, and it costs nothing to set up when you onboard the supplier.

The procurement risk factors that make organizations more exposed
Two businesses buying the same things can carry very different risk profiles. These are the factors that usually explain the difference.
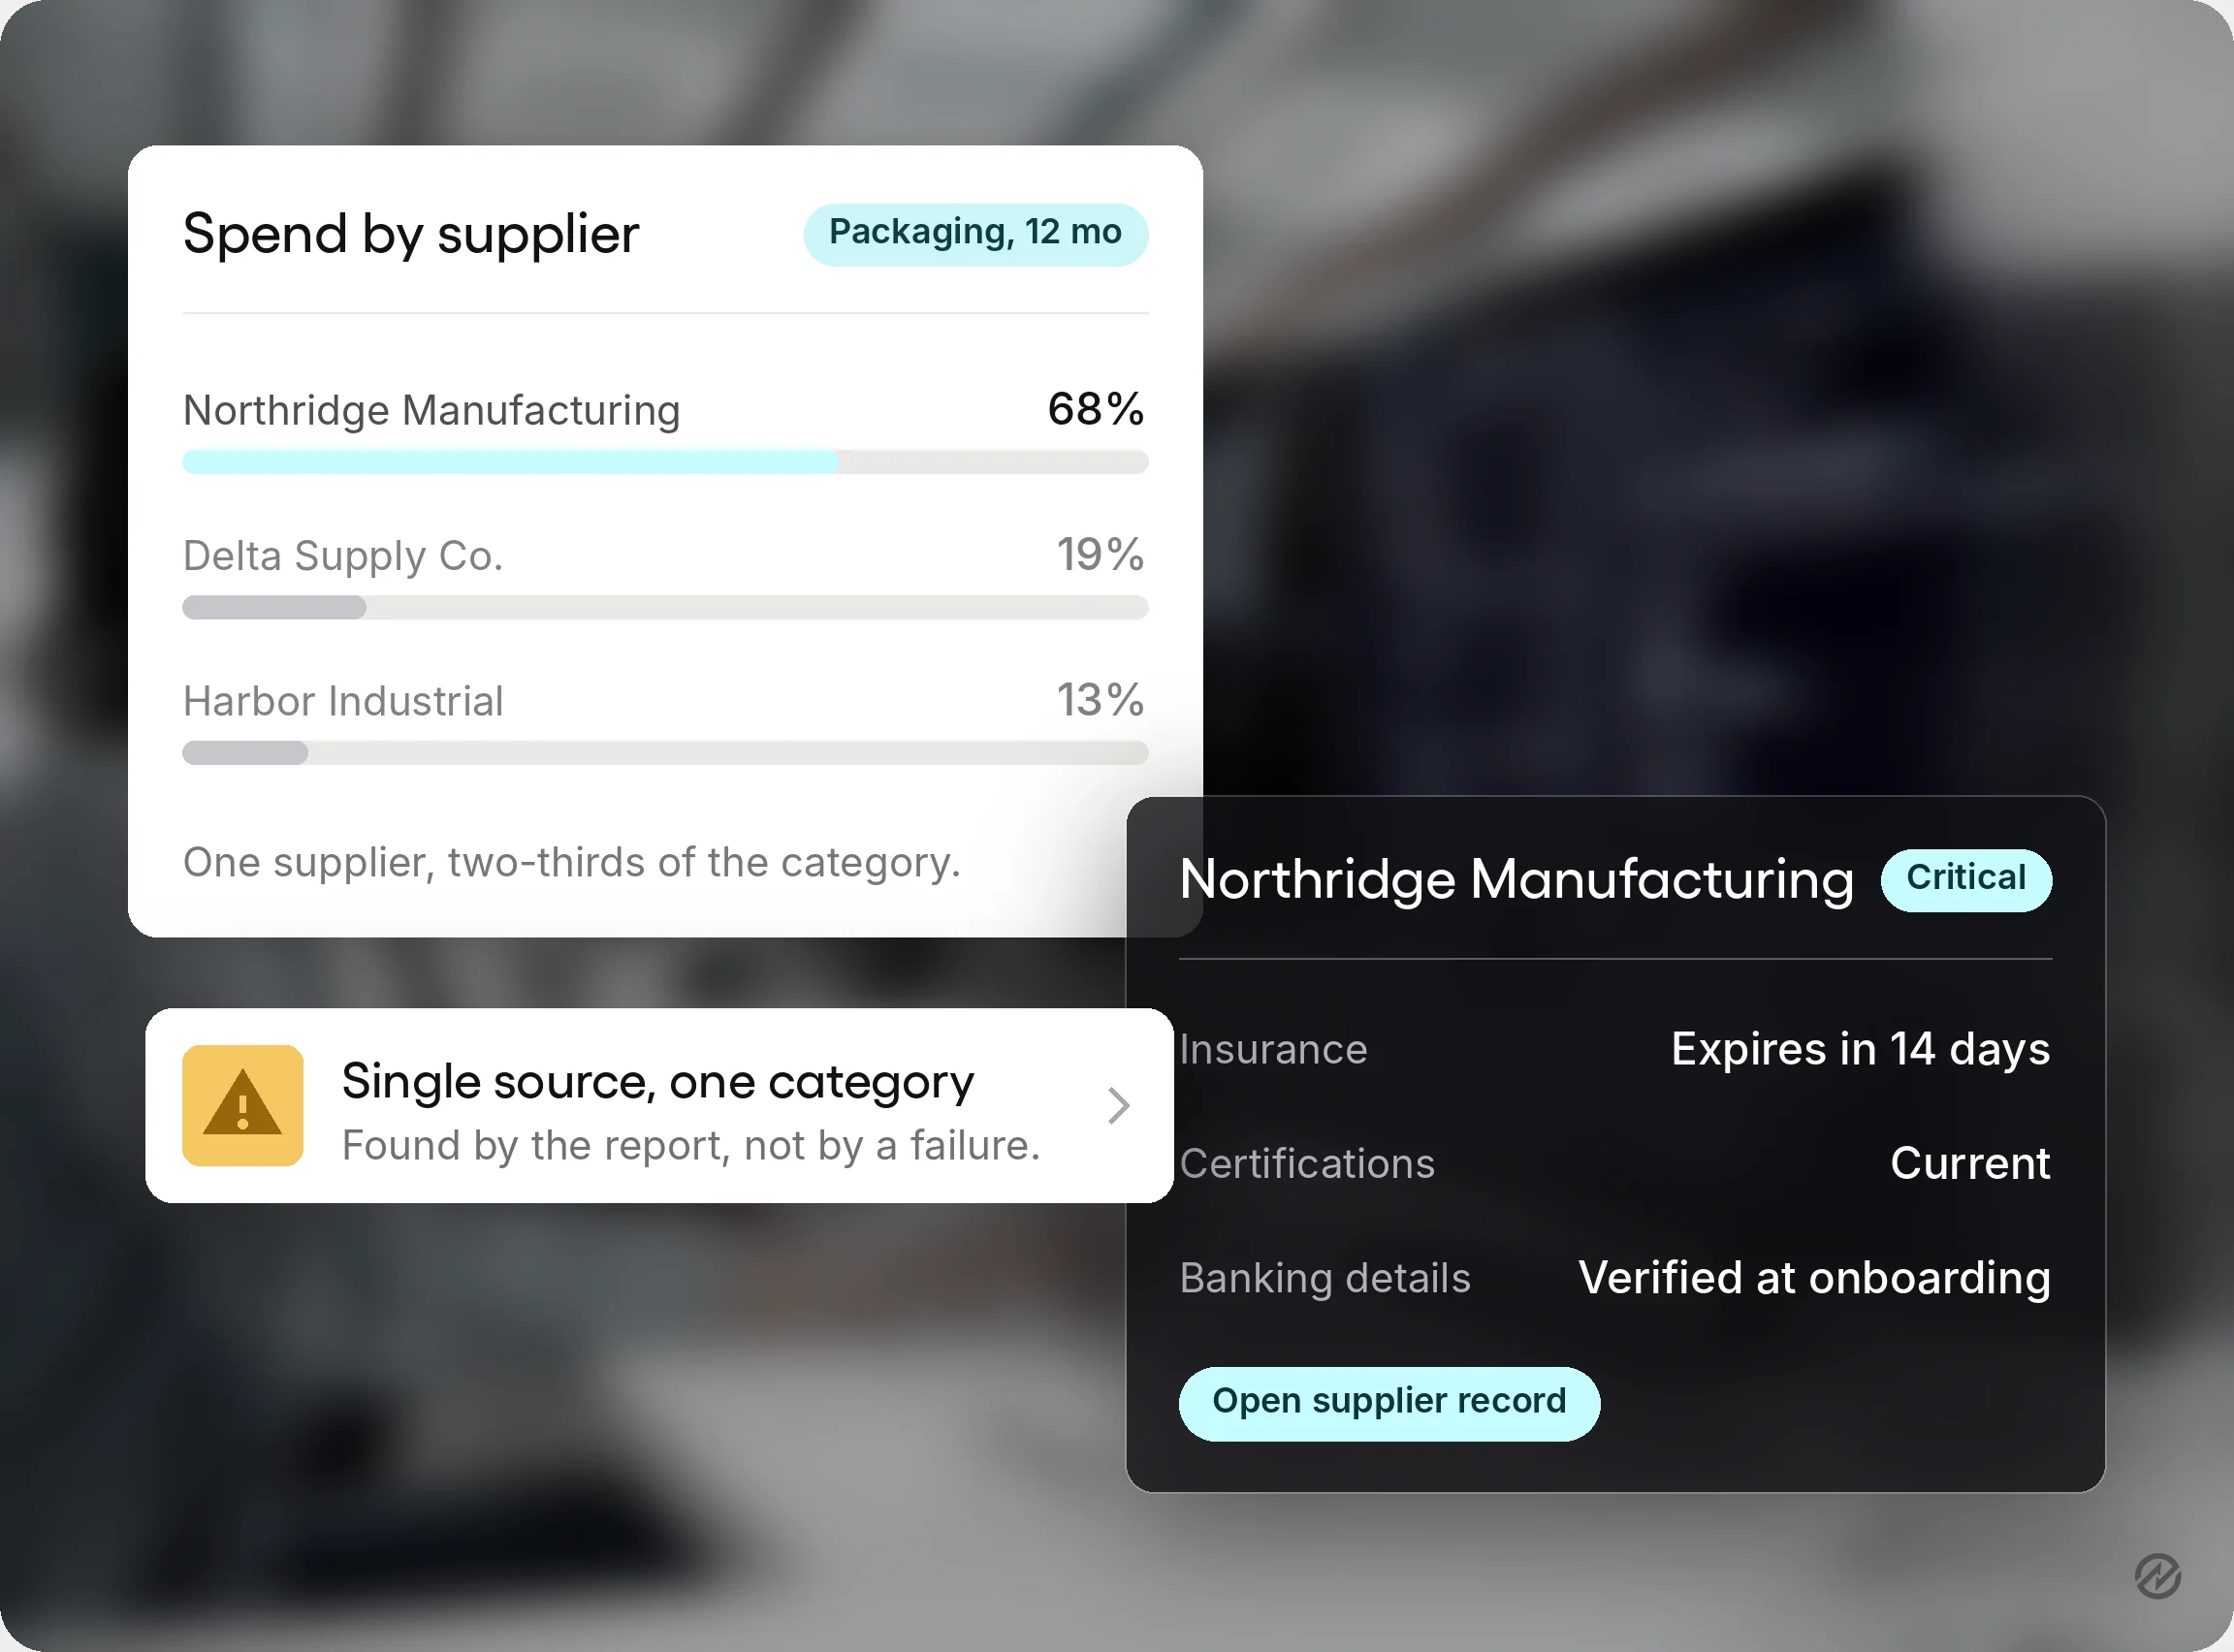
Concentration. A single supplier carrying a large share of a critical category is the most common serious exposure, and it is often invisible because nobody has looked at spend by supplier recently.
Lack of visibility. If you cannot produce a list of active contracts, expiring agreements, and committed spend within an hour, risk identification is guesswork. Many businesses run for years in this state without incident, which is not the same as being safe.
Manual processes at volume. Error rates are roughly constant per transaction, so risk scales with purchase volume. A process that was adequate at 50 orders a month is a different proposition at 500.
Unmanaged contract expiry. Agreements that lapse without review either roll over on terms nobody reviewed or leave purchasing happening with no contract at all.
No owner. Procurement risk that belongs to everyone belongs to nobody. Someone should be accountable for the risk register and for monitoring risks between reviews, even if it is part of a wider role.
Geographic and geopolitical exposure. Suppliers concentrated in one region carry correlated risk. Political developments, trade policy, and currency all move together in ways that a diversified supply base absorbs and a concentrated one does not.
Procurement contract risk management
Contracts are where procurement risk is either managed or created, and the difference is usually attention rather than legal sophistication.
Robust contract management safeguards include clear service level agreements defining acceptable performance, provisions covering delivery performance and liabilities, remedies for non-performance that are proportionate enough to invoke, price adjustment mechanics where volatility is expected, and termination rights that do not require a dispute to exercise.
What causes most contract risk is not weak drafting. It is that nobody monitors the agreement after signature. Key indicators post-contract, including whether the supplier is meeting the SLA, whether pricing matches the agreed schedule, or whether insurance and certifications remain current, are what turn a contract from a document into a control.
Three practical habits cover most of it. Keep every contract in one place with its renewal date visible, which is as much a vendor management discipline as a legal one. Set a review trigger 60 to 90 days before expiry so renewal is a decision rather than a default. And check invoices against contracted pricing rather than assuming the rate card is being applied, which is where a surprising amount of value leaks.
Building a risk management-focused procurement process
You do not need a risk function to do this well. You need four steps that actually run.
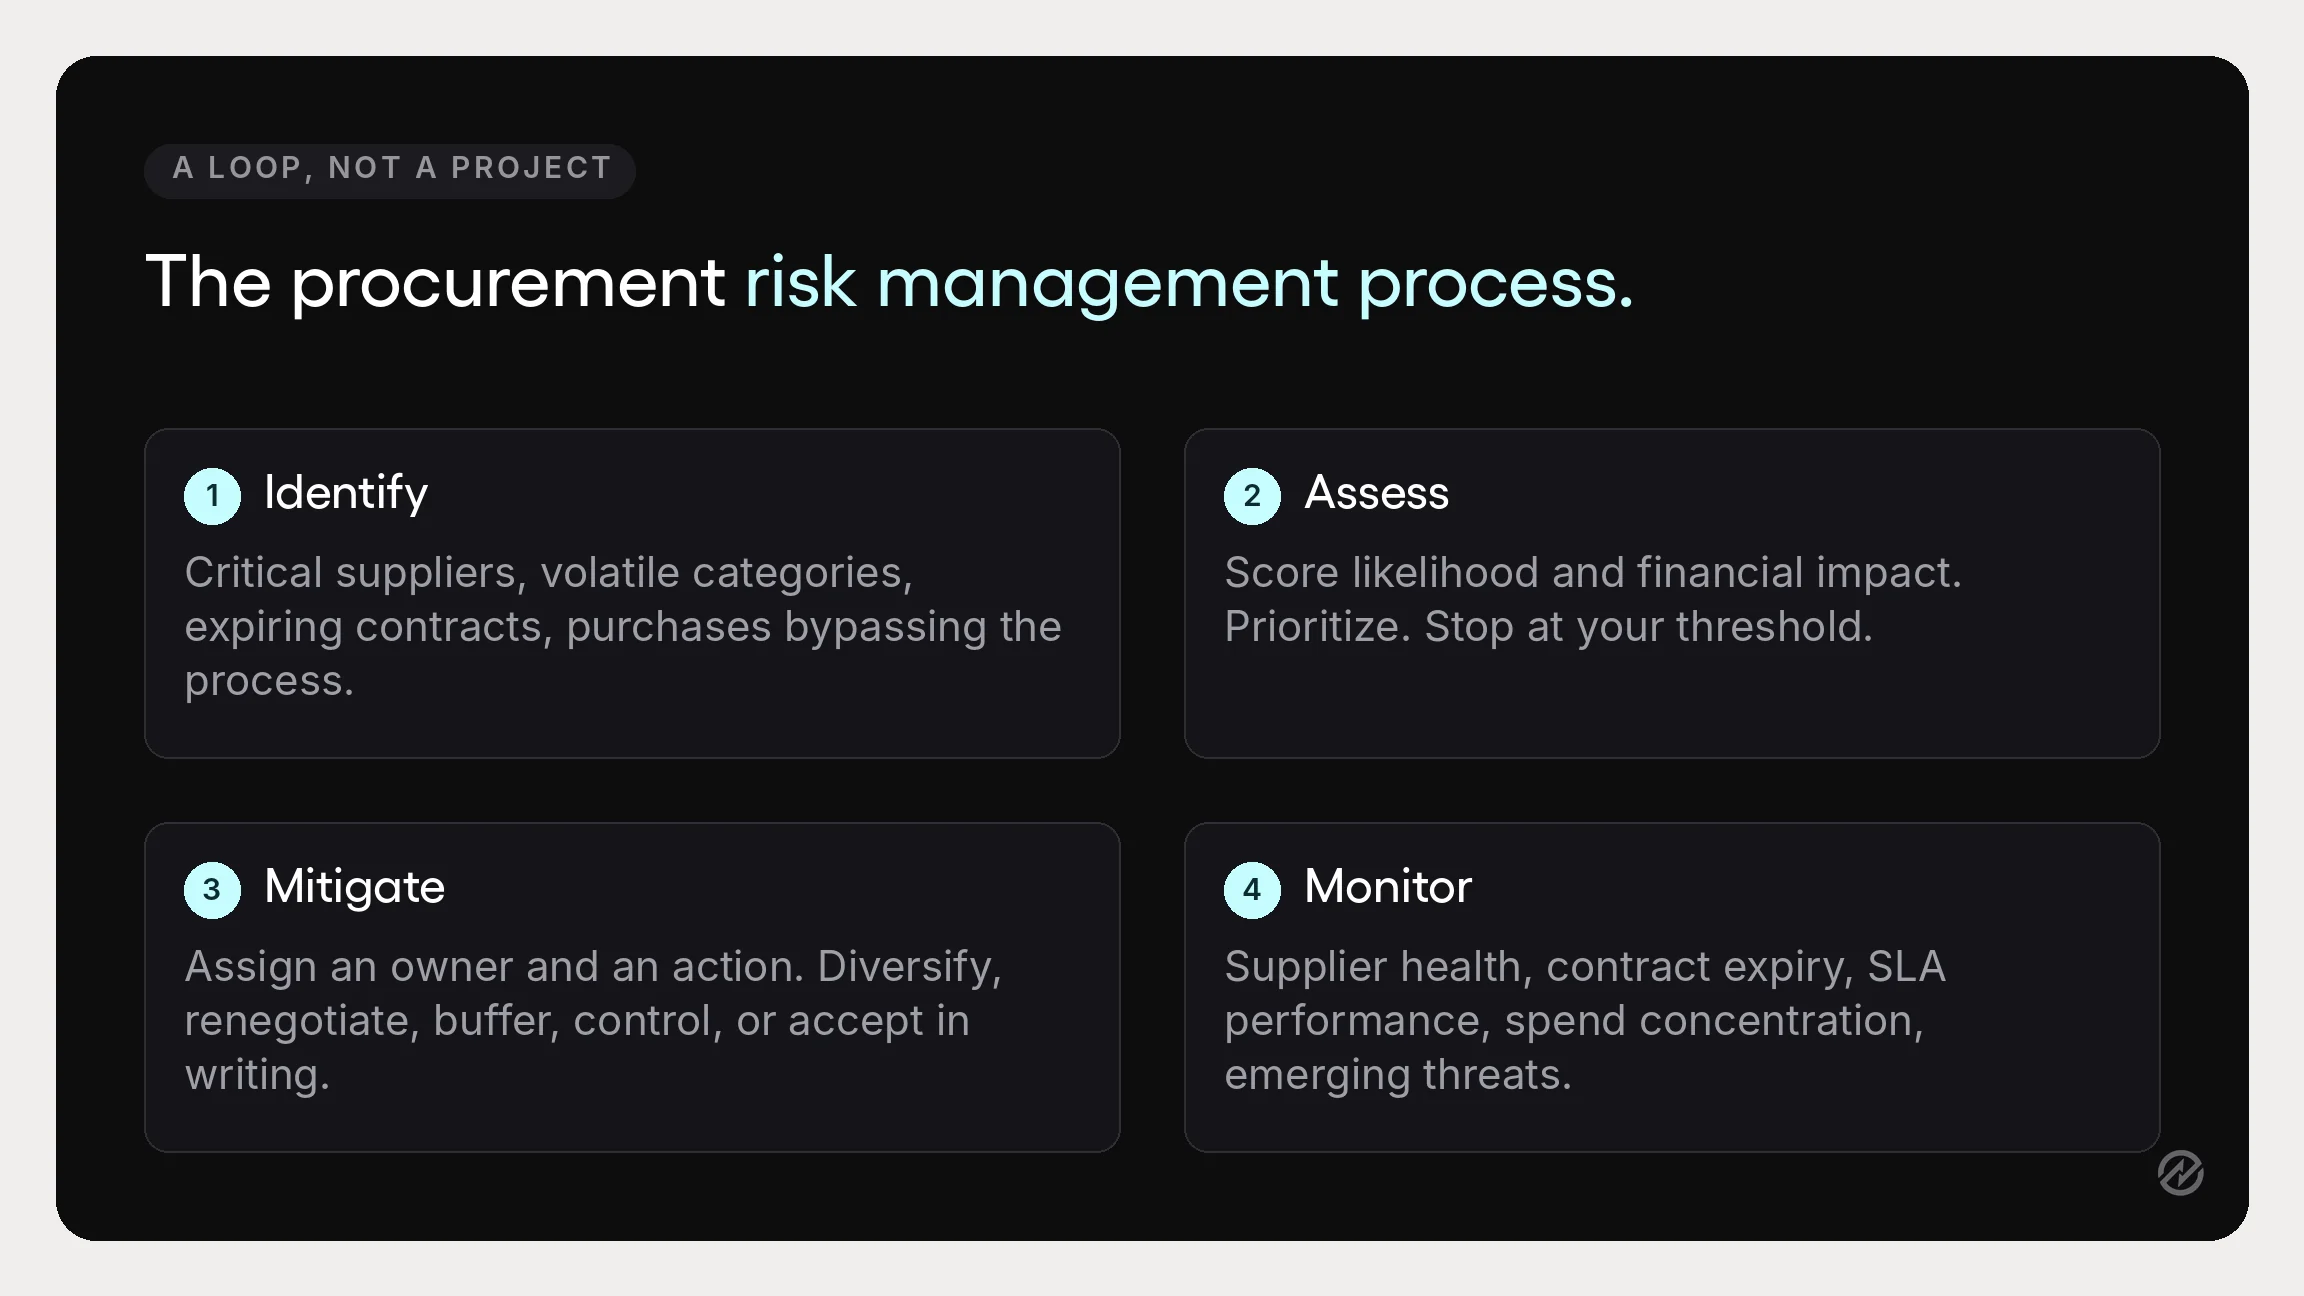
1. Identify. Map where exposure exists across the supply chain lifecycle: which suppliers are critical, which categories are volatile, which contracts are expiring, which purchases bypass the process. Cross-functional collaboration matters here, because finance, operations, and legal each see risks procurement does not.
2. Assess. A risk assessment scores each identified risk on likelihood and potential impact, with financial impact estimated rather than described. Risk analysis at this stage does not need to be sophisticated, only consistent, so that identified risks can be compared against each other. This is what allows prioritization, and prioritization is what keeps the exercise finite. Established risk management frameworks such as ISO 31000 and COSO ERM provide structure if you want it, though a defensible two-axis assessment is better than an elaborate model nobody maintains.
3. Mitigate. Assign an owner and an action to the risks that clear your threshold. Options that actually mitigate procurement risks include diversifying suppliers, renegotiating terms, building buffer stock, tightening internal controls, or deliberately accepting the risk and documenting why. Contingency plans matter most for the risks you decide to accept.
4. Monitor. Maintain a risk register and review it on a fixed cadence. Ongoing monitoring should cover supplier financial health, contract expiry, performance against SLAs, spend concentration, and emerging risks in your categories. Risk monitoring that happens annually is documentation. Risk monitoring that happens quarterly is a control.
Proportionality runs through all four steps. Critical suppliers warrant more scrutiny than low-risk ones, and a program that treats them alike will be abandoned within a year. It is also how you scale risk management as purchase volume grows without adding headcount to match.
How procurement technology reduces risk
Procurement tools do not eliminate risk. They shorten the gap between something going wrong and someone noticing, where most damage accumulates.
Visibility into commitments. A live record of what has been requested, approved, and ordered makes exposure visible before the invoice arrives, not after.
Consistent controls. The system applies approval rules, spending thresholds, and approved supplier lists every time, rather than depending on whether someone remembered.
Supplier records that support due diligence. Certifications, insurance, banking details, contracts, and performance history on one record make continuous monitoring practical rather than aspirational.
Automation of the error-prone steps. Automating requisitions, purchase order creation, and invoice matching removes the retyping that drives most operational risk and frees the procurement team to focus on judgment work.
Spend analysis that surfaces concentration. Procurement reporting by supplier and category helps uncover single-source dependencies before they become incidents, turning risk into an input to decision-making rather than a postmortem topic.
For the strategy layer above these controls, our guide to procurement strategies for risk mitigation covers the actionable approaches in more depth. For the supplier-specific view, see 5 steps for a successful supplier risk management program, and for disruption specifically, 7 supply chain risks and how to mitigate them.